aaPanel Security Notice: PHP and Node.js Updates
Critical PHP Security Update
On October 21, 2026, PHP fixed CVE-2026-109618 and CVE-2026-109619. Both are rated CVSS v4.0 9.2 and may allow unauthenticated remote code execution.
Affected environments include PHP-FPM, Apache mod_php, php-cgi, FrankenPHP and LiteSpeed. Risk is highest for Apache mod_php.
PHP Versions and Patch Availability
The latest official PHP releases containing the fixes are:
| PHP branch | Official patched release |
|---|---|
| PHP 8.5 | 8.5.12 |
| PHP 8.4 | 8.4.27 |
| PHP 8.3 | 8.3.36 |
| PHP 8.2 | 8.2.35 |
For the older branches listed below, the PHP team has made source code available through GitHub without providing prebuilt packages. aaPanel is handling the packaging of these patched builds.
These are aaPanel-provided patched builds and should not be confused with new official upstream releases.
| PHP branch | aaPanel patched build | Status |
|---|---|---|
| PHP 7.4 | 7.4.34 | Available through aaPanel |
| PHP 8.1 | 8.1.35 | Available through aaPanel |
| PHP 8.0 | 8.0.27 | Still undergoing testing; not yet available for deployment |
Availability may vary depending on your aaPanel App Store. Please refresh the application list to check for updates.
PHP Versions Earlier Than 7.4
aaPanel plans to publish updated configuration guidance tomorrow for PHP versions earlier than 7.4. WAF rules will also be updated to help block related attacks.
These configuration changes and WAF rules are mitigation measures, not replacement security patches. Users of older PHP versions should migrate to a supported release or confirm patch availability with their provider.
How to Update PHP in aaPanel
- Back up your websites, databases and configurations.
- Open App Store > Installed.
- If necessary, click Update App List to refresh available releases.
- Update every PHP version in use to the corresponding patched release or aaPanel-provided build when available.
- Restart the affected PHP services and verify that your websites work as expected.
PHP 8.0 users: The aaPanel patched build is still being tested. Please follow the official forum for its release status.
OpenLiteSpeed LSPHP Update Issue
Due to a script compatibility issue with OpenLiteSpeed, the current aaPanel script supports LSPHP installation but not upgrades.
For now, update existing LSPHP installations using your system package manager.
CentOS / AlmaLinux / Rocky Linux
yum update 'lsphp*' -y
Debian / Ubuntu
apt-get update
apt-get install --only-upgrade 'lsphp*' -y
After updating, restart the affected services and verify that your websites work correctly.
Temporary Mitigation
The following settings address specific attack paths for CVE-2026-109619 only. They do not fix both vulnerabilities or replace security updates.
The PHP official advisory recommends these settings to block confirmed session attack paths and, on PHP 8.5, the fatal error backtrace path.
For each affected PHP version, open Settings > Configuration file (php.ini) and set:
session.upload_progress.enabled = 0
For PHP 8.5, also set:
fatal_error_backtraces = 0
Restart all affected PHP workers after saving the changes.
These settings must take effect before request parsing. Do not rely on ini_set() or PHP-FPM .user.ini files to apply these mitigations.
Node.js Security Updates
Node.js fixed 10 vulnerabilities, including four high-severity issues.
Update to one of the following fixed releases:
- 22.23.4
- 24.22.1
- 26.12.1
How to Update Node.js in aaPanel
- Open Website > Node.js Project > Node version manager.
- Refresh the version list.
- Install a fixed release appropriate for your projects.
- Switch each project to the updated Node.js version.
- Restart each project and verify that it works correctly.
Installing a new Node.js version alone does not update existing projects. Each project must be switched to the new version and restarted.
Further Updates
aaPanel will continue to monitor these security issues and provide updates on PHP 8.0 testing, configuration guidance for older PHP versions and WAF rule changes.
Please follow the official aaPanel forum for release availability and further security updates.
Comments
The PHP issue had a significant impact, so we spent the entire night working to address it.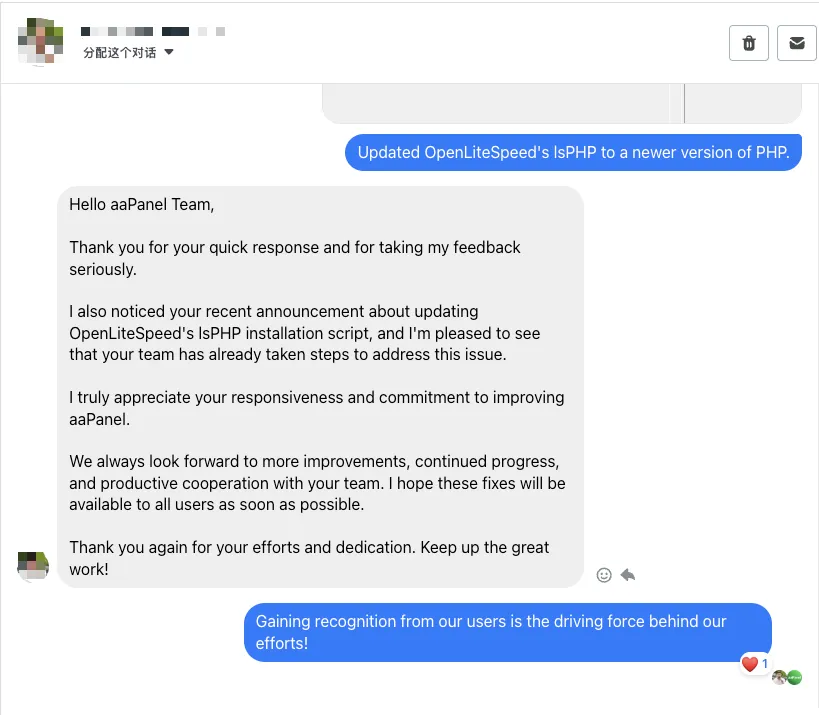
But seeing the positive feedback from our users makes all that effort worthwhile!